Automation feature to reduce man-hours for security management


4/5
Automatic blocking from network against unmanaged (privately owned/outside) PC
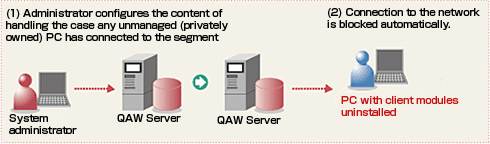
If at least one privately owned PC or outside PC is connecting to in-house network, it may deliver a big security risk for the enterprise. QAW is always monitoring in-house network, and if it found PCs connected to the network with the client modules of QAW uninstalled, it blocks them from the network automatically, as they are judged as unmanaged (privately owned/outside) PCs. It is also possible for QAW to perform automatic installation of client modules on unknown PC or to allow temporary connection manually.
Detects unregistered PC automatically
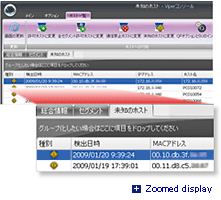
A new host detecting function has been added that enables the detection of IT devices newly connected to the network. All the nodes with MAC addresses, not only PC but also hubs, routers, etc. will be detected. At the moment of detection, PC with the client modules installed will be registered as allowed host automatically.
Blocks unregistered PC from the network automatically
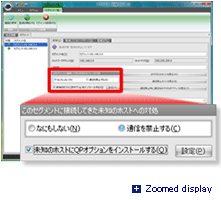
It is possible to install the client modules automatically to unregistered PC detected by QAW.
PCs that the administrator thought as illegal or unregistered PCs to which client modules cannot be installed will be judged as unmanaged, and blocked from the network automatically.
Automatic blocking from network by periodical policy check against illegitimate PC
It is possible for the system administrator to block members who have not passed the policy check from the network, by the liaison with the simple quarantine feature (SecurePolicy Manager) that QAW equips. About the operation after the rejection by policy checking, please refer to the page describing the simple quarantine feature.
>Simple Quarantine feature